
Morgan Stanley Unveils Novel Method for Phishing Detection: Optically Analyzing Deceptive Domain Names
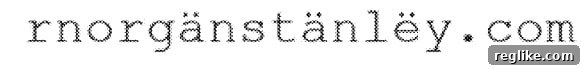
In an increasingly digital world, the threat of cybercrime, particularly phishing, poses a significant risk to individuals and organizations alike. While patent applications related to domain name security are often filed by internet security specialists, it is particularly compelling to observe a leading financial services institution like Morgan Stanley innovating in this space. The company has introduced a unique and sophisticated approach to identify domain names that are designed to trick web users, aiming to significantly enhance defenses against phishing attacks.
The Pervasive Threat of Phishing and Deceptive Domains
Phishing remains one of the most effective and widespread cyber threats, consistently evolving to bypass traditional security measures. Attackers meticulously craft fraudulent websites and communications that mimic legitimate entities, such as banks, e-commerce platforms, or popular social media sites. Their ultimate goal is to deceive users into revealing sensitive information, including login credentials, financial details, or personal data. The efficacy of a phishing campaign heavily relies on the attacker’s ability to create a credible illusion, with the domain name often serving as the primary point of deception.
Existing phishing detection systems typically employ a combination of techniques, including blacklisting known malicious domains, analyzing domain names for suspicious keywords, and evaluating domain reputation. However, these methods often fall short against the cunning tactics employed by modern cybercriminals. Two particularly problematic techniques that exploit human perception and system vulnerabilities are typosquatting and homograph attacks:
- Typosquatting: This technique involves registering domain names that are deliberate misspellings or variations of legitimate websites. For instance, attackers might register “gooogle.com” instead of “google.com” or “bankofamericaa.com” to catch users who make common typing errors. More subtly, they might use visually similar characters, like replacing the letter ‘o’ with the digit ‘0’ (“amaz0n.com”) or ‘l’ with ‘1’ (“faceb00k.com”), which are easily overlooked by the untrained eye.
- Homograph Attacks (IDN Spoofing): These sophisticated attacks leverage the visual similarities between characters from different international character sets, primarily within Internationalized Domain Names (IDNs). An attacker could register a domain such as “apple.com” where one or more Latin characters (e.g., ‘a’, ‘e’) are subtly replaced with visually identical or nearly identical characters from another script, such as Cyrillic or Greek. To the average user, the fraudulent domain appears indistinguishable from the genuine one, making detection extremely difficult for both humans and many automated systems that only process characters at a textual level.
These deceptive practices highlight a critical vulnerability: the gap between how a domain name is rendered visually and how it is processed textually by security tools. It’s a challenge that demands an innovative solution.
Morgan Stanley’s Groundbreaking Patent: “Optically Analyzing Domain Names”
To address the escalating sophistication of deceptive domain attacks, Morgan Stanley filed patent application number 16/059707, titled “Optically Analyzing Domain Names,” in 2018. The patent, which was officially published on February 13, 2020 (view the full PDF here), outlines a revolutionary method to identify domain names designed to visually trick web users, thereby flagging them as strong phishing candidates.
The core of Morgan Stanley’s innovation lies in its “optical analysis” methodology, which simulates human visual perception while retaining the rigor of automated systems. This approach moves beyond mere string comparison by treating domain names not just as text, but as visual entities. Here’s a detailed breakdown of the proposed process:
- Domain Name Image Rendering: The initial step involves converting a suspicious domain name from its textual format into various graphical representations. This means rendering the domain name as an image, mimicking how it would appear on a screen, rather than just processing its underlying character sequence.
- Application of Diverse Visual Distortions and Variations: To accurately replicate real-world viewing conditions and account for the multitude of ways a domain name might be displayed, the system applies an array of visual distortions and variations to the generated images. These can include:
- Font and Style Variations: Rendering the domain name in a wide range of fonts, sizes, weights, and styles. This is crucial because different fonts can make subtle character substitutions (e.g., ‘rn’ appearing as ‘m’) more or less obvious.
- Visual Transformations: Applying effects such as blurring, scaling, anti-aliasing, changes in color or contrast, and even simulating various display resolutions or rendering environments (e.g., different browser address bars, email clients, mobile screens).
- Contextual Emulation: Simulating how the domain would appear within different user interfaces, such as an email hyperlink, a browser’s URL bar, or a search result, further enhancing the realism of the visual analysis.
The objective is to generate a comprehensive set of visual interpretations of the domain, encompassing common rendering quirks and potential visual ambiguities.
- Optical Character Recognition (OCR) Conversion: Following the generation of these varied and distorted image representations, sophisticated Optical Character Recognition (OCR) technology is employed. The OCR engine’s task is to convert the pixels of the image data *back* into textual characters. Crucially, the OCR processes what it *perceives* visually, not necessarily the original text input. For instance, if, after rendering and distortion, the character sequence ‘cl’ optically resembles a ‘d’, the OCR might interpret it as ‘d’. Similarly, in a homograph attack, an IDN character (e.g., a Cyrillic ‘a’) that looks identical to a Latin ‘a’ might be recognized by the OCR as its Latin counterpart. This step effectively translates visual ambiguity into textual ambiguity that can be analyzed.
- Similarity Analysis against Target URLs: The final and critical step involves comparing the OCR-generated text output (or multiple outputs, given the array of rendering variations) against a predefined set of legitimate, target URLs. These target URLs typically belong to the organization implementing the defense (e.g., Morgan Stanley’s official domains) or other high-value entities frequently targeted by phishing. Advanced similarity algorithms, such as Levenshtein distance, Jaccard index, or more sophisticated visual similarity metrics, are used to quantify how closely the “optically analyzed” domain matches a known legitimate domain. A high degree of similarity in this visual-to-textual comparison would strongly indicate that the analyzed domain is a phishing candidate, designed to deceive users visually.
This innovative methodology directly tackles the complexities introduced by visually deceptive characters, offering a robust defense layer that traditional string-based pattern matching often overlooks. It bridges the gap between how humans perceive URLs and how machines analyze them.
Why Financial Institutions Are at the Forefront of Cybersecurity Innovation
Morgan Stanley’s proactive engagement in such specialized cybersecurity research is a reflection of its critical position in the global financial landscape. Financial institutions are perpetually among the most attractive targets for cybercriminals due to the immense value of the assets they manage and the highly sensitive nature of the client data they hold. A successful phishing attack against a financial services company can lead to:
- Significant Financial Losses: Through direct theft, fraudulent transactions, or sophisticated account takeovers.
- Severe Reputational Damage: Eroding customer trust, investor confidence, and brand credibility in a highly competitive sector.
- Strict Regulatory Penalties: Non-compliance with stringent data protection and cybersecurity regulations can result in substantial fines and legal repercussions.
- Legal Liabilities: Stemming from data breaches, customer harm, and class-action lawsuits.
Given these high stakes, financial institutions are compelled to invest heavily in cutting-edge security measures, often pioneering new techniques to stay several steps ahead of evolving threats. Developing proprietary solutions like the one outlined in this patent allows them to craft security protocols precisely tailored to their unique risk profile, ensuring the robust protection of their vast client base from increasingly sophisticated social engineering and visual deception tactics.
Broader Implications and Benefits for Global Web Security
The potential impact of Morgan Stanley’s optical analysis patent extends far beyond the financial sector, promising to significantly bolster cybersecurity across a diverse array of industries and for the general public:
- Enhanced Brand Protection: Companies across all sectors can more effectively detect and neutralize domain abuse that targets their brand, thereby safeguarding their customers from falling victim to scams impersonating their services.
- Improved User Safety: Integrating such advanced analysis capabilities into web browsers, email clients, endpoint security solutions, or web filtering services could provide real-time, proactive warnings to users before they interact with or click on deceptive domains, significantly reducing successful phishing attempts.
- Proactive Threat Intelligence: This system could be deployed to continuously scan newly registered domains for phishing potential, thereby establishing an early warning system for emerging threats and allowing security teams to mitigate risks before they materialize into widespread attacks.
- Robust IDN Security: It offers a much-needed, powerful solution for the complex security challenges posed by Internationalized Domain Names, which have historically presented a significant blind spot for many conventional text-based security tools.
- Reduced False Negatives: By intelligently mimicking human visual perception, the system is designed to catch highly sophisticated deceptive domains that might effortlessly bypass purely algorithmic or text-based security checks, thus reducing the number of missed threats.
While the computational resources required for such extensive image rendering and OCR analysis could be substantial, particularly for large-scale deployments, the resultant gains in security and user protection are invaluable, especially in high-stakes environments where the cost of a single successful phishing attack can be catastrophic.
The Continuous Battle Against Cyber Deception
This innovative patent from Morgan Stanley serves as a powerful testament to the relentless and dynamic battle between cyber attackers and defenders. As malicious actors continually devise new methods to exploit human psychology and uncover technological loopholes, cybersecurity professionals must match and exceed this ingenuity with continuous innovation.
The optical analysis method represents a critical advancement in phishing detection, moving security systems closer to an ability to understand and interpret visual cues in the nuanced and often deceptive way a human might. It strongly underscores the enduring importance of a multi-layered security strategy, which seamlessly combines cutting-edge technological defenses with robust, ongoing user education.
Ultimately, by strategically leveraging technologies like advanced image rendering and sophisticated OCR, organizations can construct significantly more resilient defenses against the increasingly intricate forms of phishing and brand impersonation. This patent application highlights a crucial paradigm shift towards more adaptive, intelligent, and visually aware cybersecurity solutions that are fully capable of addressing the nuanced and often visually driven tactics employed by today’s most dangerous cyber threats, thereby fostering a safer and more trustworthy online environment for everyone.