
Unraveling the Mystery: When a Retargeted Ad Shows You a Domain You Already Own
In the expansive and often perplexing world of digital advertising, encountering a retargeted ad has become a commonplace experience for internet users. These ads, powered by sophisticated tracking technologies, are designed to follow your online activity, serving up highly relevant products or services based on your recent browsing history. Imagine searching for a specific pair of running shoes on a retail website; it’s almost guaranteed that you’ll later see advertisements for those exact shoes popping up on unrelated sites you visit. This seamless, data-driven approach often feels remarkably useful, almost as if the internet is anticipating your needs. However, what happens when this intricate system delivers an ad so precisely targeted that it seemingly knows more about your digital assets than you’d expect, sparking both curiosity and significant privacy questions?
The Pervasive Power of Retargeting Ads
Retargeting, also known as remarketing, is a powerful advertising strategy that helps businesses reach users who have previously interacted with their website or mobile app. The core mechanism typically involves placing a small piece of code, often referred to as a “pixel” or “cookie,” on a user’s browser when they visit a particular site. This cookie acts as a digital breadcrumb, anonymously marking the user’s visit and specific actions (like viewing a product, adding an item to a cart, or even just browsing a category). Later, as that user navigates to other websites across the internet that are part of an ad network, the retargeting platform recognizes the cookie and serves up relevant advertisements from the initial site they visited. This creates a continuous engagement loop, reminding potential customers about their previous interests and encouraging them to return and complete a purchase or action. While incredibly effective for driving conversions, the underlying data collection and tracking methods raise important discussions about user privacy and data security.
An Unexpected Encounter: An Ad for My Own Domain
While the utility of retargeting is generally understood, the system occasionally produces an outcome that blurs the lines between helpful targeting and an unsettling breach of personal digital knowledge. Recently, I encountered such an instance that left me thoroughly puzzled. While browsing a website, an advertisement appeared, prominently featuring a domain name: ExecutivePay.com. The visual presentation of the ad, accompanied by text encouraging registration, immediately caught my attention. The reason for this instant intrigue was simple: I already own ExecutivePay.com. The domain had been acquired some time ago through a domain drop, a process where an expired domain becomes available for registration again.
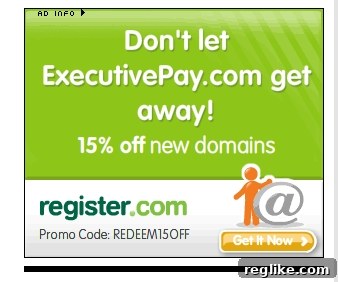
This situation was far from the typical retargeting scenario where an ad reminds me of shoes I considered buying. Instead, it was an ad for an asset I demonstrably possessed. The immediate question that sprung to mind was profoundly unsettling: How could an advertiser possibly know about my ownership of this specific domain, or at least be so closely associated with my recent online activity to serve such a specific, yet ultimately redundant, advertisement?
Initial Theories: Deconstructing the Ad’s Origins
To understand how such an ad could manifest, several hypotheses immediately came to mind. The most concerning initial thought revolved around the potential for an advertising cookie to somehow access or interpret data related to my domain ownership. Domain ownership details are publicly available through WHOIS lookups, which provide information such as the registrant’s name, contact details, and registrar. The thought that advertising cookies might be “picking up” or tracking these sensitive WHOIS searches, and then using that information for targeting, presented a significant privacy red flag. If user activities on WHOIS lookup sites were being harvested and utilized for commercial advertising, it would represent a substantial erosion of expected online privacy, particularly for individuals who frequently research domain names for business or personal reasons.
Another avenue of investigation focused on the history of the domain itself. Given that ExecutivePay.com was acquired as a dropped domain, it had a previous life. My initial thought was that perhaps I had been cookied by a registrar like Register.com (the apparent advertiser) during a period when the domain was either registered with them or while I was in the process of transferring it. However, a quick check of the domain’s historical records revealed that its previous registrar was Network Solutions, not Register.com. This finding immediately debunked the theory of a direct, long-standing cookie relationship with the advertising registrar based on the domain’s transfer history.
Unpacking the Domain Ownership vs. Availability Check Nuance
Upon closer inspection, the phrasing of the ad itself provided a crucial nuance. The advertisement didn’t explicitly state, “You own ExecutivePay.com, but you should still register it.” Instead, it functioned as a call to action to “register ExecutivePay.com before it’s too late.” This distinction is paramount. It suggested that the ad might not be directly targeting me because I own the domain, but rather because I had recently performed an availability lookup for it, or an action perceived as such. In the domain world, checking availability or performing a WHOIS query are common activities for prospective buyers, investors, or even current owners monitoring their assets.
Therefore, a more refined theory emerged: I might have performed a domain lookup, perhaps to check its WHOIS record, its status, or its potential value, on a platform or registrar website that was directly or indirectly affiliated with the company running the advertisement. If that specific website placed a cookie on my browser, indicating my interest in “ExecutivePay.com,” then the subsequent ad from Register.com would logically appear. From the advertiser’s perspective, this interaction signals intent to register, regardless of actual current ownership, making the ad technically relevant to my recent online activity, even if factually misleading in its premise for an existing owner.
The Privacy Predicament: Tracking Domain Searches
Regardless of the precise mechanism, the broader issue of advertising cookies tracking domain-related searches, especially WHOIS lookups, remains a significant privacy concern. WHOIS data can contain personal information, and the act of searching for domains is often undertaken with an expectation of a certain level of privacy. If ad networks or registrars are logging these queries and using them for targeted advertising, it could lead to several problematic scenarios:
- Sensitive Information Exposure: While the ad itself doesn’t expose personal data, the underlying tracking mechanism implies that my interest in specific domains is being cataloged and monetized.
- Competitive Intelligence: For businesses or individuals researching new domain names for projects, having that interest immediately broadcast through ads could inadvertently tip off competitors.
- Misleading Ads for Owners: As demonstrated by my experience, current domain owners might be barraged with ads for domains they already possess, creating a frustrating and irrelevant user experience.
- Erosion of Trust: When users feel their deeply specific online actions, such as researching domain ownership, are being monitored for advertising purposes, it erodes trust in online platforms and advertising practices.
This highlights the ongoing tension between personalized advertising, which aims to be helpful and relevant, and user privacy, which demands control over one’s digital footprint. The line between what’s considered “publicly available information” (like WHOIS data) and what constitutes “private browsing activity” becomes increasingly blurred in this context.
The Revelation: A First-Party Cookie Connection
Fortunately, the mystery ultimately found a less concerning, yet equally illuminating, resolution. A key detail that initially eluded recall eventually surfaced: I had indeed visited Register.com recently. My purpose for this visit was to investigate how premium domain listings, particularly those offered through platforms like Afternic (which is owned by GoDaddy, a major registrar), were displayed and integrated within a prominent registrar’s interface. Afternic facilitates the sale of premium domain names, which can include both new “brandable” domains and previously registered domains being resold at a premium price.
During my exploration on Register.com, it is highly probable that I performed a search for “ExecutivePay.com” or a similar term to see if it was listed as an Afternic premium domain, or simply to observe the user experience of a domain lookup on their site. While I owned the domain, it is technically possible for it to be listed as a “premium domain” for sale by its owner (or through a brokerage) even if it’s already registered. In the eyes of Register.com’s system, a search for “ExecutivePay.com” would trigger the perception of interest in registering or acquiring that domain. Since my visit and subsequent search activity took place directly on Register.com’s website, any cookie placed on my browser would have been a first-party cookie – originating from the site I was actively visiting.
This explanation significantly mitigates the initial privacy concerns. A first-party cookie from Register.com tracking my activity on their own site is a standard practice in web analytics and targeted advertising, albeit one that still feeds into retargeting efforts. It is far less problematic than the alternative scenario where a third-party cookie, potentially from a WHOIS lookup service or another unrelated site, might have been covertly collecting and sharing my sensitive domain search data across different platforms. The distinction between first-party and third-party cookies is crucial here; while both track user behavior, first-party tracking is generally viewed as more transparent and less invasive, as it directly relates to a user’s interaction with a specific website.
Navigating the Complexities of Digital Advertising
My experience with the ExecutivePay.com ad serves as a powerful reminder of the intricate and often opaque nature of digital advertising. It underscores several key takeaways for both consumers and businesses operating in the online space:
- Cookie Awareness is Key: Users should be more aware of how cookies track their activity, distinguishing between first-party cookies (set by the website you visit) and third-party cookies (set by other domains, often for advertising). Regularly reviewing and managing browser cookie settings can provide greater control.
- Privacy Implications of All Online Activity: Even seemingly innocuous actions, like checking domain availability or browsing specific listings, can leave a digital trail that informs advertising algorithms. Users should consider the privacy implications of every click and search.
- Advertiser Responsibility: While retargeting is effective, advertisers have a responsibility to refine their targeting parameters to avoid irrelevant or potentially unsettling ads. Continuously improving algorithms to differentiate between “checking availability” and “owning” could enhance user experience.
- The “Available” Paradox: The concept of a domain being “available” can be multifaceted, especially with premium listings. A domain might be registered but still “available” for purchase through a secondary market or broker. This complexity can sometimes lead to confusing ad scenarios.
Conclusion: Learning from a Targeted Ad
What began as a perplexing encounter with an ad for a domain I already owned evolved into a valuable lesson in the mechanics of modern digital advertising and the nuances of online privacy. While the initial concern about widespread WHOIS tracking was ultimately alleviated by recalling a specific first-party interaction, the incident highlighted the potential for such systems to misinterpret user intent and raise legitimate privacy questions. As our digital lives become increasingly intertwined with sophisticated tracking technologies, understanding how our online actions translate into targeted advertisements is more crucial than ever. It encourages both users to be more vigilant about their digital footprint and advertisers to strive for greater transparency and accuracy in their personalization efforts, ensuring that convenience doesn’t come at the cost of trust or privacy.