
Navigating the Labyrinth of Look-Alike Domains: Understanding Homoglyph Confusion
In the vast and often intricate landscape of the internet, clarity is paramount. Yet, an insidious form of visual deception frequently causes confusion: the uncanny resemblance of certain characters, particularly the lowercase ‘L’ and the uppercase ‘I’. This subtle typographic quirk can lead to significant misunderstandings, financial losses, and even security vulnerabilities, especially within the realm of domain names.
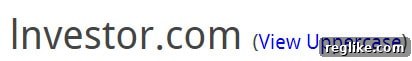
The issue recently came into sharp focus with a notable incident that underscored just how easily these characters can be confused. A bit of a ruckus emerged when NameJet, a prominent domain auction platform, promoted what appeared to be the highly valuable domain “Investor.com” for sale. However, as eagle-eyed observers soon discovered, the domain was actually “Lnvestor.com,” featuring a lowercase ‘L’ at the beginning instead of an uppercase ‘I’. The font utilized by NameJet, in this specific instance, rendered the lowercase ‘L’ in a manner almost indistinguishable from its uppercase ‘I’ counterpart, creating a perfect storm of typographic ambiguity.
This isn’t an isolated incident, nor is it a novel problem. Before casting stones, it’s worth noting that even experienced domain professionals can fall prey to this visual trick. The author, for instance, recounts a personal anecdote from a few years prior, having made the exact same mistake. A backorder was placed on “Lnternational.com” under the mistaken belief that it was the legitimate “International.com.” Such experiences highlight the inherent difficulty in distinguishing these characters at a glance, especially when the context is familiar and expectations are already set.
The Pervasive Threat of Homoglyph Domains and Online Impersonation
The problem extends far beyond simple typographical errors. Malicious actors frequently exploit this ‘L’ versus ‘I’ trick, along with other similar character substitutions, to engage in nefarious activities. Remember the fake domain broker that was attempting to peddle domains at seemingly too-good-to-be-true prices? They leveraged precisely this L vs. I trick to deceive potential buyers, selling them worthless or misrepresented assets while masquerading as legitimate entities. This tactic is a classic example of typosquatting or homograph attacks, where fraudsters register domains that visually mimic legitimate ones, hoping to trick users into divulging sensitive information, downloading malware, or making fraudulent purchases.
The stakes are particularly high for businesses and brand owners. A domain name is often the cornerstone of a company’s online identity. When look-alike domains surface, they can severely damage a brand’s reputation, dilute its online presence, and divert valuable traffic. Consumers, unaware of these subtle distinctions, might inadvertently land on a phishing site, believing they are interacting with a trusted brand. The financial and reputational fallout from such incidents can be devastating, underscoring the critical need for vigilance and robust protection strategies.
The Global Dimension: Internationalized Domain Names (IDNs) and Enhanced Confusion
If the ‘L’ vs. ‘I’ confusion seems problematic, imagine the complexities introduced by Internationalized Domain Names (IDNs). IDNs allow domain names to contain characters from non-Roman alphabets, such as Cyrillic, Arabic, or Chinese. While IDNs are crucial for global inclusivity and accessibility, they also open a Pandora’s Box of potential for homoglyph attacks.
Many characters from different scripts bear an uncanny resemblance to Latin characters. For example, the Cyrillic ‘а’ looks identical to the Latin ‘a’, and the Cyrillic ‘р’ can be mistaken for the Latin ‘p’. A malicious actor could register a domain like “apple.com” using Cyrillic characters that look exactly like their Latin counterparts. To the unsuspecting eye, “аpple.com” (with a Cyrillic ‘a’) appears indistinguishable from “apple.com” (with a Latin ‘a’). This technique is known as an IDN homograph attack or “punycode” attack, as these domains are represented in the Domain Name System (DNS) using a special encoding called Punycode (e.g., `xn--pple-4xa.com`).
For individuals who are not familiar with the nuances of internationalized domain names, discerning such a subtle difference is virtually impossible. They might purchase what appears to be a valuable domain, only to discover later that some of the characters are not from the Roman alphabet, rendering the domain less valuable, difficult to manage, or even inherently malicious. The consequences can range from a simple wasted investment to becoming a vector for sophisticated phishing campaigns against unsuspecting users. This global layer of complexity elevates the ‘L’ vs. ‘I’ problem from a typographic inconvenience to a significant cybersecurity concern affecting users worldwide.
Best Practices and Proactive Solutions for Platforms and Users
Given the persistent nature of homoglyph confusion, both domain platforms and individual users must adopt proactive measures to mitigate risks. For platforms like NameJet, there’s a clear opportunity for user experience enhancement. While NameJet currently offers an option to ‘view upper case’ next to the domains, this requires an extra click and implies the user is already suspicious. Realizing this might be an edge case for some, a more robust solution would be to present domain names in a way that explicitly highlights potential ambiguities.
A simple yet effective solution would be for platforms to display both the uppercase and lowercase versions of the domain name by default, or at least to visually flag characters known for high homoglyph potential. For instance, instead of just showing “Lnvestor.com,” it could display “Lnvestor.com (L/l)” or provide a direct, clear visual distinction if a specific font makes ‘l’ and ‘I’ look identical. Some advanced systems might even employ algorithms to detect highly confusable characters and issue warnings to users, perhaps displaying the Punycode equivalent alongside the human-readable IDN to raise awareness.
For domain investors, thorough due diligence is non-negotiable. Before investing in any domain, especially those that appear similar to highly valuable names, it’s crucial to verify every character. Copy-pasting the domain into a text editor where different fonts can be tested, or using online tools that analyze domain characters for homoglyph potential, can help prevent costly mistakes. Always be suspicious of deals that seem “too good to be true,” as they often hide such deceptive character substitutions.
For the average internet user, vigilance is key. Always scrutinize URLs, especially in emails or messages that prompt sensitive actions like login or payment. Before clicking a link or entering credentials, hover over the URL to see its true destination, and mentally (or even physically) double-check characters that appear ambiguous. Browser security features and extensions that warn about suspicious domains or display Punycode for IDNs can also provide an added layer of protection.
The Continuous Battle for Clarity in a Digital World
The challenge of distinguishing visually similar characters in domain names is a microcosm of the broader struggle for clarity and security in our increasingly complex digital world. As technology evolves and the internet becomes more diverse with IDNs, the potential for deceptive practices also grows. It’s a continuous cat-and-mouse game between those who exploit ambiguity and those who strive to create a safer, more transparent online environment.
The responsibility to address this issue is shared. Domain registrars and registries must implement stricter policies and develop better tools to prevent the registration of highly confusable domains, or at the very least, clearly mark them. Browser developers should continue enhancing security warnings and improving how IDNs are displayed to make homograph attacks more difficult to execute and easier for users to identify. And, critically, users themselves must cultivate a habit of skepticism and verification, understanding that what appears on screen may not always be what it seems.
In conclusion, the simple visual confusion between ‘L’ and ‘I’ serves as a powerful reminder of the subtle vulnerabilities that exist within our digital infrastructure. While seemingly minor, these distinctions can have significant consequences, ranging from misinformed domain investments to widespread phishing attacks. By implementing proactive measures on platforms and fostering greater awareness among users, we can collectively work towards a more secure and transparent internet, where deceptive character tricks are rendered ineffective.
Oh, and on a related note, be on the lookout. I don’t think I ever renewed Lnternational.com after my initial backorder attempt, but it has remained in my Enom count anyway. It expires later this month and will make its way through the drops. Perhaps a valuable lesson in what *not* to acquire, but a continuous reminder of the persistent challenge of look-alike domains.