
Members of ICANN community and competing domain registrars find themselves as new United Domains account holders.
United Domains Confronts Security Challenge Following Mass Prank Account Creation
A recent and rather peculiar incident has cast a spotlight on the delicate balance between user convenience and robust security within the domain name registration industry. In what has been described as a sophisticated, yet seemingly non-malicious, prank, an unidentified perpetrator orchestrated the creation of approximately 500 phantom accounts at the prominent domain name registrar, United Domains. The most striking detail of this incident lies in the chosen targets: email addresses belonging to influential members of ICANN’s Governmental Advisory Committee (GAC) and various professionals at competing domain name registrars. Each of these unwitting individuals subsequently received an unexpected welcome email from United Domains, confirming their new, unauthorized account status.
The Genesis of the Incident: A Widespread Digital Prank
Over the past few days, a wave of unsolicited welcome emails from United Domains reached an eclectic mix of individuals across the domain name landscape. These weren’t random occurrences; they targeted specific, publicly accessible email addresses associated with key players in internet governance and the competitive domain registration market. The sheer scale of the operation—around 500 fabricated accounts—points towards a systematic and deliberate effort rather than an isolated, accidental misstep. The perpetrator clearly aimed to make a statement, however playful, at United Domains’ expense, igniting discussions about online account security and the ease of digital identity creation.
The selection of targets is particularly noteworthy. ICANN’s Governmental Advisory Committee (GAC) serves as a vital advisory body to the ICANN Board, offering counsel on public policy matters related to the Internet’s domain name system. Its members typically represent national governments, public authorities, and international governmental organizations, and their contact details are often made public to facilitate transparency and communication within the global internet community. Similarly, many professionals employed by competing domain registrars have their business contact information readily available online. This widespread public accessibility of email addresses appears to have been exploited by the orchestrator of this prank, inadvertently highlighting a potential vulnerability where easily discoverable data can be leveraged for mass account creation on digital platforms.
United Domains’ Official Stance: Assessing Motives and Mitigating Concerns
Upon realizing the extent of this unusual activity, United Domains acted swiftly to address the situation. The company promptly distributed an email to all individuals whose email addresses were implicated in the unauthorized account setup. This communication served to acknowledge the incident, provide clarification, and reassure recipients that the matter was under investigation. The immediate goal was to allay any anxieties regarding potential identity theft or more serious, malicious intent.
According to Kate Hutchinson, Marketing Manager for United Domains, the company’s initial internal assessment suggests that the perpetrator’s motives were primarily mischievous rather than sinister. “Someone thought it would be fun,” Hutchinson commented, downplaying the severity of the act itself. She further elaborated that United Domains does not believe the incident is connected to identity theft, an assertion bolstered by the fact that all the email addresses used in this extensive prank were already publicly available online. This ease of access to such public information underscores a persistent challenge for companies seeking to verify user identities without introducing overly burdensome or complex registration processes that could deter legitimate users.
The Paradox of Simplicity: United Domains’ Slogan Under Scrutiny
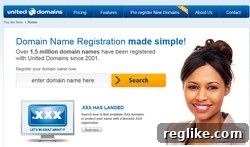
This incident has, perhaps inadvertently, brought the core philosophy of United Domains into sharp focus. The company’s prominent website slogan, “Domain Name Registration made simple!”, perfectly encapsulates its commitment to delivering a streamlined and user-friendly experience. A fundamental aspect of this commitment is the straightforward process by which anyone can create an account on their platform. However, the recent mass prank suggests that this dedication to simplicity might have inadvertently created an open door for misuse. The current threshold for accountability during the account creation phase appears to have been sufficiently low to allow for such an organized, albeit seemingly harmless, act to occur without significant immediate barriers.
The tension between offering a seamless, friction-free user experience and implementing robust, layered security measures is a perennial challenge faced by all online service providers. This dilemma is particularly acute for businesses operating in sensitive sectors like domain name registration, where the integrity of digital identities is paramount. While an effortlessly simple registration process is highly appealing to legitimate users, it can simultaneously create exploitable avenues for various forms of abuse. This incident serves as a compelling reminder that even seemingly innocuous pranks can unveil underlying vulnerabilities within a system, prompting a re-evaluation of existing security protocols.
Immediate Measures and Future Security Enhancements
Recognizing the broader implications of this incident, United Domains has committed to taking proactive steps to fortify its security infrastructure. Kate Hutchinson confirmed that the company is actively implementing significant modifications to its existing account creation process. “We are making some changes to how you can create an account that will require a higher level of accountability,” Hutchinson stated, signaling a clear intent to enhance the robustness of their system. While specific technical details of these upcoming enhancements have not yet been publicly disclosed, it is reasonable to anticipate the integration of industry-standard security features designed to introduce more stringent verification steps for new users. The aim is to deter not only similar future pranks but also more serious, potentially malicious threats.
These anticipated changes are likely to encompass a range of widely adopted security practices, which may include:
- Mandatory Email Verification: Requiring new users to click on a unique link sent to their registered email address to activate their account, thereby confirming ownership and preventing unauthorized email usage.
- Integration of CAPTCHA/reCAPTCHA: Implementing automated challenges designed to distinguish between genuine human users and automated bots, significantly reducing the potential for script-based account creation.
- Offering Two-Factor Authentication (2FA): Providing or, in some cases, mandating an additional layer of security beyond a traditional password, such as a one-time code sent to a mobile device, to enhance account protection.
- Enhanced IP Address Monitoring: Implementing sophisticated systems to detect and flag unusual patterns of account creation originating from a single or suspicious IP address, indicative of automated or malicious activity.
- Implementing Rate Limiting: Enforcing restrictions on the number of accounts that can be created from a single IP address or within a defined timeframe, preventing rapid, large-scale account generation.
- Consideration of Identity Verification: For certain services, higher-value transactions, or specific levels of access, exploring more robust identity verification checks to confirm the legitimacy of users.
Broader Implications for the Domain Industry and Cybersecurity Landscape
This incident, though characterized as a “fun” prank, carries significant broader implications that resonate throughout the domain name industry and the wider online security landscape. For domain registrars, maintaining the unwavering trust of their user base and ensuring the unimpeachable integrity of their services are paramount objectives. Any perceived vulnerability, even if exploited solely for a joke, can subtly but steadily erode customer confidence. This event serves as an urgent reminder for all registrars to consistently review, rigorously test, and proactively update their security measures, particularly those governing the initial point of contact for users: the account creation process.
Furthermore, it vividly underscores the persistent challenges associated with digital identity management and the potential misuse of publicly available personal information. In our increasingly interconnected digital world, where professional contact details are frequently accessible across various platforms, companies bear the crucial responsibility of developing and deploying systems robust enough to prevent their platforms from being exploited. This obligation extends even to scenarios where the exploitation appears to be for seemingly harmless ends. The demarcation between a benign prank and a serious security vulnerability can often be exceptionally fine, and what might commence as a trivial joke could potentially escalate, revealing previously unseen pathways for future, more sophisticated, and truly malicious cyberattacks.
The incident also provides a valuable opportunity for introspection regarding the importance of robust personal security practices, not just for corporations but for individual internet users as well. While United Domains is actively implementing necessary changes, individuals are simultaneously encouraged to maintain heightened vigilance regarding unsolicited emails and to promptly report any suspicious digital activity. The fundamental integrity of the internet’s vast infrastructure, encompassing everything from domain registration systems to everyday email services, ultimately relies on a collective and unwavering commitment to robust security protocols and responsible digital citizenship from all stakeholders.
Conclusion: A Critical Learning Curve for United Domains
What initially materialized as a peculiar prank involving 500 unauthorized accounts and prominent figures within the ICANN community has rapidly evolved into a pivotal learning experience for United Domains. While the company has taken steps to assure the public that the incident was not driven by malicious intent, it has undeniably exposed a discernible weakness within their existing account creation framework. The prompt and decisive response from United Domains, coupled with their explicit commitment to integrating higher levels of accountability into their systems, represents a positive and crucial step towards fortifying their overall security posture. This event serves as a critical, timely reminder to all online service providers that in the ever-evolving digital realm, striking the optimal balance between providing seamless user convenience and implementing stringent, multi-layered security protocols is not merely an optional consideration, but an absolute and indispensable necessity for maintaining trust, safeguarding user data, and ensuring the long-term operational integrity of their platforms.