
Cisco’s Innovative Patent: Revolutionizing Typosquatting Detection with IP Information
In the vast and ever-expanding digital landscape, brand integrity and user safety are paramount. Yet, lurking within the corners of the internet is a pervasive threat known as typosquatting – the practice of registering domain names that are misspellings or slight variations of legitimate brands. This deceptive tactic aims to lure unsuspecting users, often leading to phishing scams, malware infections, or simple brand dilution. For years, detecting and combating typosquatting has been a resource-intensive challenge for businesses and cybersecurity professionals alike. However, a recent patent granted to Cisco marks a significant leap forward, offering a more efficient, safer, and remarkably intelligent approach to identifying these malicious domains: by leveraging Internet Protocol (IP) information.
Cisco’s Groundbreaking Patent: A New Era in Domain Security
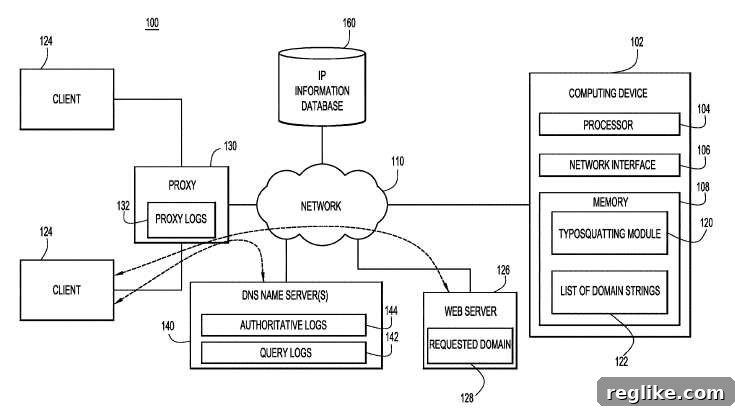
Cisco, a global leader in networking hardware and telecommunications equipment, has been granted U.S. Patent Number 10,491,614 for “Illegitimate typosquatting detection with internet protocol information.” This patent introduces a sophisticated methodology that moves beyond traditional, often cumbersome, detection techniques. Historically, identifying typosquatting domains frequently involved visiting the suspicious domain name, a risky endeavor that could expose the investigator to malicious code, phishing attempts, or other cyber threats. Cisco’s innovative approach circumvents these dangers by focusing on the underlying IP information rather than the content hosted on the domain.
The core of Cisco’s invention lies in its ability to analyze and compare the IP addresses associated with potential typo domains. Instead of rendering web page content, which consumes significant time and resources and carries inherent risks, the system evaluates where these domains resolve on the internet. This fundamental shift in strategy provides a swift, secure, and scalable method for vetting vast numbers of suspicious domain registrations. By focusing on the network layer, Cisco’s technology promises to drastically improve the speed and safety of typosquatting detection, offering organizations a proactive defense mechanism against digital threats.
Distinguishing Between Friend and Foe: Legitimate vs. Illegitimate Typosquatting
One of the most compelling “novelties” of Cisco’s patent is its capacity to differentiate between what the inventors term “illegitimate typosquatting” and “legitimate typosquatting.” This distinction is critical because not all domain misspellings are created equal; some are actually part of a legitimate brand protection strategy, while others are designed for malicious purposes. Traditional detection methods often struggle to make this nuanced differentiation, leading to false positives and wasted investigative efforts. Cisco’s IP-based system offers a clear, objective metric to separate benign defensive registrations from actively harmful ones.
Understanding Legitimate Typosquatting: Defensive Strategies for Brand Protection
Many prominent companies and brand owners proactively register various misspelled versions or common typographical errors of their official domain names. This practice, known as defensive registration or legitimate typosquatting, serves several vital purposes. It acts as a preventative measure, ensuring that malicious actors cannot seize these closely related domains and exploit them. Furthermore, these defensively registered domains are often configured to redirect traffic back to the legitimate, correct website, thereby capturing users who might have made a simple typing error and guiding them to the intended destination. This not only preserves brand reputation but also prevents lost traffic and potential customer confusion.
Cisco’s patent identifies a simple yet powerful indicator for legitimate typosquatting: the IP address. If a typo domain name resolves to the same IP address as the legitimate domain, or to an IP address known to be controlled by the legitimate brand owner (e.g., pointing to their official hosting provider or a dedicated defensive redirect service), it is highly likely to be a legitimate defensive registration. By recognizing these patterns, the system avoids flagging benign domains as threats, allowing security teams to allocate their resources more effectively and focus solely on genuine risks. This intelligent filtering significantly reduces the noise and improves the signal in typosquatting alerts, making domain monitoring more efficient and less prone to errors.
Unmasking Illegitimate Typosquatting: Identifying Malicious Domain Impersonations
In stark contrast to legitimate defensive registrations, illegitimate typosquatting involves the registration of typo domains with malicious intent. These domains are typically set up by cybercriminals or competitors to engage in a variety of harmful activities. Common objectives include phishing, where users are tricked into divulging sensitive information such as login credentials or financial details; distributing malware by prompting unsuspecting visitors to download infected files; generating illicit advertising revenue through forced redirects or ad-heavy content; or even damaging a brand’s reputation by hosting offensive or misleading material. The financial and reputational damage caused by illegitimate typosquatting can be substantial, making its detection and mitigation a top priority for businesses.
Cisco’s IP-based detection method excels at identifying these nefarious activities. When a typo domain resolves to an IP address that is different from the legitimate brand’s IP, it immediately raises a red flag. Further analysis can then be performed on this distinct IP address. For instance, if the IP address has a known history of hosting malicious content, belongs to a suspicious network range, or is geographically located in an unusual or high-risk region for the legitimate brand, these are strong indicators of illegitimate intent. This method provides a reliable, non-intrusive way to quickly determine if a typo domain poses a genuine threat, allowing security teams to take immediate action without exposing their systems to potential dangers by directly accessing the malicious site.
The Power of IP: Technical Advantages and Enhanced Cybersecurity
The technical advantages of Cisco’s IP-centric approach to typosquatting detection are manifold. Firstly, it offers unparalleled speed. IP resolution is a fundamental network operation, allowing for the rapid processing of massive lists of potential typo domains. Unlike content-based analysis, which requires fetching and parsing potentially complex web pages, IP lookups are nearly instantaneous. Secondly, safety is dramatically enhanced. By not needing to visit or render content from suspicious domains, the risk of accidental malware infection, drive-by downloads, or exposure to exploit kits during the detection process is completely eliminated. This makes the investigative process inherently secure.
Furthermore, the system boasts exceptional scalability. Organizations can monitor hundreds of thousands, or even millions, of potential typo domains without overwhelming their resources or infrastructure. This makes it a powerful tool for large enterprises with extensive brand portfolios. Accuracy is also a significant benefit; IP correlation provides strong, objective evidence regarding the ownership and intent behind a domain. This patent represents a foundational element that can be integrated into broader cybersecurity frameworks, enhancing DNS firewalls, threat intelligence platforms, and automated security orchestration solutions. By providing a clear, actionable signal about domain legitimacy, it empowers security systems to block malicious traffic at the network edge, protecting users before they ever encounter a threat.
Beyond Detection: The Broader Impact on Brand Trust and Digital Safety
Cisco’s patent for IP-based typosquatting detection is more than just a technical innovation; it’s a strategic enhancement for brand protection and overall digital safety. In an era where digital presence is synonymous with business identity, safeguarding against domain impersonation is crucial for maintaining customer trust and ensuring business continuity. Proactive identification of illegitimate typo domains allows brands to swiftly issue cease-and-desist letters, file domain disputes, or work with registrars to take down malicious sites, thereby mitigating potential damage before it escalates.
Moreover, this technology contributes to a safer internet for everyone. By making it easier and safer for organizations to detect and combat typosquatting, it indirectly reduces the attack surface available to cybercriminals. Users are less likely to fall victim to phishing scams or malware if the deceptive domains are identified and neutralized before they can cause harm. As cyber threats continue to evolve in sophistication, innovative solutions like Cisco’s IP-based detection become indispensable tools in the ongoing battle to protect digital assets and foster a more secure online environment for businesses and consumers alike.
Strengthening the Digital Frontier: Cisco’s Vision for a Safer Internet
In conclusion, U.S. Patent Number 10,491,614 represents a significant milestone in cybersecurity. Cisco’s invention of “Illegitimate typosquatting detection with internet protocol information” provides a smarter, safer, and more scalable method for an enduring digital threat. By moving beyond risky content-based analysis to a robust IP-centric approach, the patent not only refines the detection process but also introduces a critical distinction between legitimate defensive registrations and malicious impersonations. This innovation empowers organizations to safeguard their brands, protect their users, and streamline their cybersecurity operations, ultimately contributing to a more resilient and trustworthy digital ecosystem.