
Domain Name Hijacking: Twitter, New York Times, and MelbourneIT
The digital landscape recently witnessed alarming incidents where the domain names of prominent websites, including Twitter and The New York Times, were reportedly compromised. These incidents underscore the persistent threat of domain hijacking and the critical need for robust security measures to protect valuable online assets. A common thread linking these high-profile cases is their shared use of MelbourneIT, a domain name registrar.
The compromise of a domain name can have far-reaching consequences, potentially disrupting website accessibility, redirecting traffic to malicious sites, and damaging brand reputation. For organizations like Twitter and The New York Times, which rely heavily on their online presence, such incidents can lead to significant financial losses, reputational damage, and erosion of user trust.
The New York Times Domain Record
Following the reported incidents, an examination of The New York Times’ WHOIS record revealed concerning alterations. The WHOIS record, a public database containing information about registered domain names, serves as a vital source for verifying domain ownership and contact details. Any unauthorized modification to this record raises red flags and indicates a potential domain compromise.
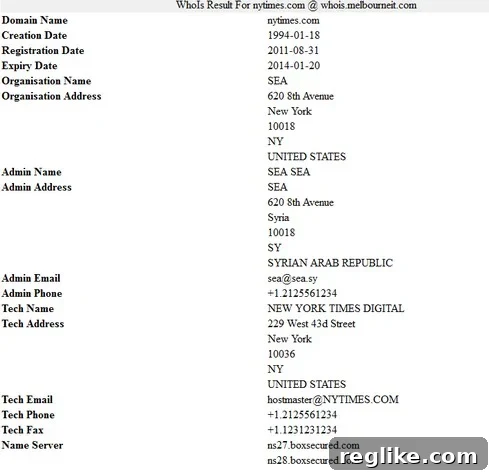
A snapshot of The New York Times’ WHOIS record showing potential modifications.
The altered WHOIS record raised immediate concerns about the security of The New York Times’ domain and the potential for malicious actors to exploit the compromised domain for nefarious purposes. This incident highlights the vulnerability of even well-established organizations to domain hijacking attacks and the importance of continuous monitoring and proactive security measures.
Twitter’s DNS and Alleged Compromise
While the WHOIS record for Twitter appeared to be intact when checked through MelbourneIT, reports surfaced alleging that the company’s Domain Name System (DNS) records had been compromised earlier that day. DNS records are essential for translating domain names into IP addresses, enabling users to access websites. If DNS records are manipulated, users can be redirected to fraudulent websites, even if they type the correct domain name into their browser.
The Next Web reported the alleged compromise, suggesting that the Syrian Electronic Army (SEA) may have been responsible. The SEA, a pro-Assad hacking group, has been linked to numerous cyberattacks targeting media organizations and other entities critical of the Syrian government. While the alleged DNS compromise was reportedly addressed quickly, the incident served as a stark reminder of the ongoing threat posed by politically motivated cyberattacks.
Huffington Post UK: Another Potential Target?
Adding to the concerns, reports also circulated suggesting that the Huffington Post’s UK site may have experienced a domain name compromise. Although this could not be immediately confirmed, it was noted that the Huffington Post UK, like Twitter and The New York Times, also utilizes MelbourneIT for its domain registration. This further fueled speculation about a potential vulnerability within MelbourneIT’s systems or a targeted attack against its clients.
The Role of Domain Registrars and Security Measures
Domain registrars play a crucial role in the security of domain names. They are responsible for verifying the identity of domain owners, maintaining accurate WHOIS records, and implementing security measures to prevent unauthorized access and modification of domain settings. When domain registrars fail to adequately protect their systems, they become a prime target for cybercriminals seeking to hijack domain names.
In light of the reported incidents affecting Twitter, The New York Times, and potentially the Huffington Post UK, it is imperative that domain registrars prioritize security and implement robust measures to safeguard their clients’ domain names. These measures should include:
- Two-Factor Authentication (2FA): Implementing 2FA for all registrar accounts adds an extra layer of security by requiring users to provide two forms of authentication, such as a password and a code sent to their mobile device. This makes it significantly more difficult for hackers to gain unauthorized access to registrar accounts.
- Regular Security Audits: Conducting regular security audits helps identify vulnerabilities in registrar systems and processes. These audits should be performed by independent security experts and should cover all aspects of the registrar’s infrastructure, including web servers, databases, and network devices.
- Intrusion Detection and Prevention Systems: Implementing intrusion detection and prevention systems (IDPS) helps monitor network traffic for malicious activity and automatically block suspicious connections. These systems can detect and prevent a wide range of cyberattacks, including SQL injection, cross-site scripting (XSS), and brute-force attacks.
- Strong Password Policies: Enforcing strong password policies requires users to create complex passwords that are difficult to crack. These policies should also encourage users to change their passwords regularly.
- Employee Training: Providing employees with comprehensive security training helps them recognize and avoid phishing attacks and other social engineering techniques. Employees should be trained on how to identify suspicious emails, websites, and phone calls.
- DNS Security Extensions (DNSSEC): Implementing DNSSEC helps protect against DNS spoofing attacks by digitally signing DNS records. This ensures that users are connecting to the legitimate website and not a fraudulent copy.
- Domain Locking: Domain locking prevents unauthorized transfers of domain names to other registrars. This feature can be enabled by domain owners to prevent their domains from being hijacked by malicious actors.
- WHOIS Privacy Protection: WHOIS privacy protection hides the personal information of domain owners from the public WHOIS database. This helps protect domain owners from spam, phishing attacks, and identity theft.
The Importance of Proactive Security
The recent domain name compromises serve as a wake-up call for organizations of all sizes. It is no longer sufficient to rely solely on the security measures provided by domain registrars. Organizations must take a proactive approach to security and implement their own safeguards to protect their valuable online assets. This includes:
- Monitoring DNS Records: Regularly monitoring DNS records for unauthorized changes can help detect and prevent DNS hijacking attacks. Organizations can use various tools to monitor their DNS records and receive alerts when changes are detected.
- Implementing Multi-Factor Authentication: Implementing multi-factor authentication for all critical accounts, including registrar accounts, email accounts, and social media accounts, can significantly reduce the risk of unauthorized access.
- Educating Employees: Educating employees about phishing attacks and other social engineering techniques can help prevent them from falling victim to these scams.
- Regularly Backing Up Website Data: Regularly backing up website data can help organizations recover quickly from a cyberattack. Backups should be stored in a secure location that is separate from the main website.
- Having a Cyber Incident Response Plan: Having a well-defined cyber incident response plan can help organizations respond quickly and effectively to a cyberattack. The plan should outline the steps to be taken to contain the attack, restore data, and notify affected parties.
Conclusion: A Call to Action
The domain name compromises affecting Twitter and The New York Times highlight the critical need for robust security measures to protect valuable online assets. Domain registrars must prioritize security and implement strong safeguards to prevent unauthorized access and modification of domain settings. Organizations must also take a proactive approach to security and implement their own safeguards to protect their websites and data. By working together, domain registrars and organizations can create a more secure online environment for everyone.