America phishing scam shows limitations of validated TLDs — Bank of
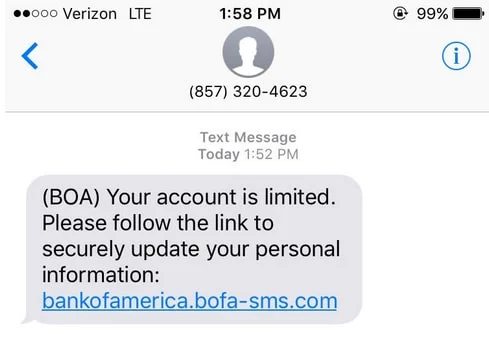
People will fall for this bogus domain name.
Domain investor Abdu Tarabichi sent a screenshot of a text he received today from a scammer:
If you go to the subdomain of BofA-SMS.com it will ask you to unlock your account by entering your credit card number, expiration date, CVV and the last four digits of you SSN.
I’m sure people will fall for this scam, and it’s a reminder of one of the broken promises of what fresh top level domain names can offer.
Some peddlers of fresh TLDs argued that firms could cut down on phishing by getting a .brand top level domain name. When consumers see a .brand domain such as .bofa, they’d know they were at the right site, the argument goes. Therefore, they won’t get phished anymore.
The problem with this argument is that seeing the valid TLD is a positive. People get phished by the negative: not noticing that it’s the incorrect URL.
Validated TLDs such as .bank (podcast) have a similar problem.
By the way, BofA-SMS.com has a public whois but it appears to be false. The phone number transfers to an international dial tone and then goes to voicemail.
The same user is also associated with BofA-txt.com as stated by DomainIQ.