Domains to thwart botnets — Microsoft registers
Microsoft registers domains previously used by Citadel malware.
Microsoft has registered a number of domain names to thwart a cybercrime ring credited with over a half billion dollars in financial fraud.
The action aims to thwart Citadel malware, which installs keyloggers on users’ machines. The malware and crime ring had over 1,000 botnets.
Although Microsoft’s press release regarding its actions against Citadel doesn’t mention domains, an attachment to the lawsuit filed against the perpetrators includes a list of over 4,000 domain names linked to Citadel.
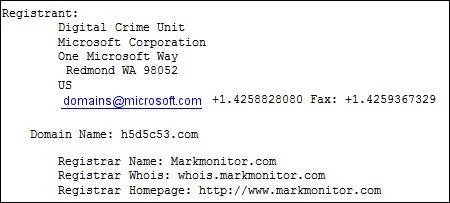
Service providers appear to have by now suspended many of the registered domain names. But some of the domains on the list were unregistered. Microsoft has proactively registered these domains to its “Digital Crime Unit”.
In response to an inquiry from Reglike, Richard Boscovich, Assistant General Counsel, Microsoft Digital Crimes Unit wrote:
The other domains were previously documented as being used by Citadel, but the cybercriminals had stopped using them and many had expired registrations. Since these domains were previously connected to the threat, and available, we registered them as a precautionary measure.
Here’s an example of a whois of one of the proactively registered domains, h5d5c53.com:
You can see a full list of the 4,000+ domains here (pdf).