Mimicking a firm’s whois record to hide a cybersquatting domain
An odd whois record gets me thinking.
I was going through my daily check of notable domain name transfers when I came across something curious.
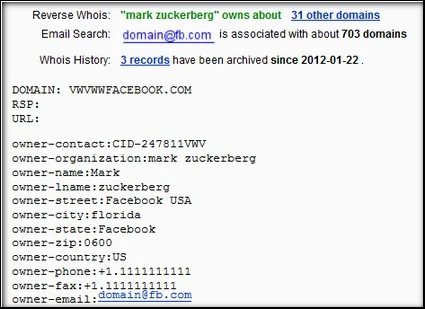
The whois record for vwvwwfacebook.com changed from someone in Turkey to this whois:
I’ve followed a lot of handovers of domains from cybersquatters to Facebook, and this one seems odd. The email address now associated with the domain is indeed the one that Facebook uses for newly transferred domains. But it doesn’t put them in Mark Zuckerberg’s name, nor is it based in Florida. And of course the phone number and address are bogus. The nameservers haven’t changed either.
It’s possible that Facebook does own this domain now, but I doubt it. This seems like a rather clever way to keep a corporation off your back if you own a typo of their trademark.
If the domain gets added to the firm’s hit list, they’ll look up the whois and see that they “own” it. If it’s just a parked domain they may drop the issue there. If it’s something else, they may log in to their registrar accounts to see if they have control of the domain. If they catch on, they’ll just transfer the domain to themselves using the admin email address (assuming it’s not locked).
I want to be clear here that I’m not condoning doing something like this. I’m curious if anyone seen similar cases of whois spoofing?