
The Double Standard: Why Large Corporations Advocate Against WHOIS Privacy They Use Themselves
In the vast and interconnected digital landscape, domain name registration data, often referred to as WHOIS information, serves as a public record of who owns a website. It contains critical details such as the registrant’s name, address, email, and phone number. For decades, the accessibility of this information has been a cornerstone of internet transparency, crucial for everything from combating cybercrime to enforcing intellectual property rights. However, a persistent and perplexing paradox exists within this ecosystem: why do so many large corporations vehemently lobby against WHOIS privacy and proxy services, while simultaneously leveraging these very tools to mask their own domain registrations?
This question, frequently raised by industry observers like Kevin Murphy, highlights a deep vein of hypocrisy that runs through the corporate world’s stance on internet transparency. While these companies often champion the need for open WHOIS data to protect their brands, pursue online infringers, and ensure accountability, their actions tell a different story. They often employ sophisticated methods to shield their own domain acquisitions from public scrutiny, creating a clear “do as I say, not as I do” dynamic that undermines their stated principles.
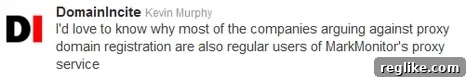
Indeed, it is undeniable that WHOIS privacy services can be abused for nefarious purposes. Cybercriminals, spammers, and malicious actors often hide their identities to evade detection and accountability. This legitimate concern is frequently cited by corporations when they argue for the abolition or significant curtailment of privacy services. However, to broadly label all WHOIS privacy as inherently “bad” ignores the myriad of legitimate reasons, both individual and corporate, for wanting to keep registration details confidential. When large entities adopt this sweeping condemnation while actively engaging in their own forms of domain stealth, the argument rings hollow and exposes a significant double standard.
The Legitimate Case for Corporate Domain Privacy
Beneath the surface of corporate criticism, there are genuinely strategic and competitive reasons why businesses, including the largest conglomerates, opt to use WHOIS privacy or proxy services. These reasons are often tied to highly sensitive business operations that, if revealed prematurely, could severely impact market dynamics, stock prices, or competitive advantage.
Strategic Product Launches and Business Initiatives
One of the most common and widely accepted legitimate uses for corporate domain privacy is during the development and launch of new products, services, or significant business initiatives. Imagine a multinational tech company developing a revolutionary new gadget. Registering domains related to this product months in advance is a crucial step in securing intellectual property and preparing for market entry. If these registrations, complete with the company’s direct contact information, were immediately public, competitors could gain early insight into their plans, potentially rushing similar products to market, manipulating stock prices, or initiating counter-marketing campaigns. By using an affiliated proxy service, such as MarkMonitor’s DNStination, Inc., companies can secure these vital digital assets without signaling their intentions to the entire industry. While the use of specific nameservers might occasionally give clues, the initial stealth registration remains a powerful tool.
Mergers, Acquisitions, and Market Sensitivity
Another critical scenario involves mergers, acquisitions, and other market-sensitive corporate actions. Discussions and preparations for such events are often shrouded in intense secrecy. Acquiring domain names pertinent to a potential merger target or a new subsidiary can be a necessary precursor to finalizing a deal. Publicly linking these domains to either company before an official announcement could lead to insider trading, speculation, market instability, or even jeopardize the entire deal by alerting competitors or regulatory bodies prematurely. WHOIS privacy in these instances serves as a vital safeguard for corporate value and integrity.
Protection Against Corporate Espionage and Employee Harassment
Beyond competitive maneuvers, corporations also utilize privacy services to protect themselves and their employees from various threats. Corporate espionage is a real and constant danger, and direct WHOIS contact information can be a vulnerability that malicious actors exploit. Furthermore, in an age where public figures and executives are increasingly targeted, protecting personal and corporate contact details linked to domain registrations can mitigate risks of harassment, doxing, or other forms of targeted attacks against individuals within the company. This layer of anonymity, therefore, is not about avoiding accountability but about enhancing security and operational resilience.
The Dubious Side of Corporate Domain Stealth
While legitimate uses for WHOIS privacy abound, the corporate world is not immune to exploiting these services for less ethical, or even nefarious, purposes. It is these instances that fuel the criticism and underscore the hypocrisy when companies simultaneously advocate for complete transparency.
Suppressing Negative Information: The Guthy-Renker Example
A prominent example illustrating the questionable use of WHOIS privacy involves Guthy-Renker, the company behind the popular Proactiv acne treatment. In a particularly telling incident, the company registered a multitude of domain names related to a product recall. These domains were registered under MarkMonitor’s DNStination, Inc., effectively obscuring Guthy-Renker’s direct association. Initially, one might assume this was a strategic move to prepare for a public announcement without causing premature panic. However, it soon became clear that the intentions were far more problematic.
Instead of merely reserving domains like ProactivRecall.com for an official statement, Guthy-Renker’s objective was to keep crucial information about the recall out of the public domain. While a less obvious domain, PAbottlereplacement.com, did use the company’s corporate information (though it was stealthy and non-indexed), the more direct and public-facing recall domains were deliberately hidden. This strategy aimed to control the narrative by limiting the avenues through which consumers could find information about a potentially problematic product. Such actions directly contradict the principles of corporate responsibility and transparency, especially concerning public health and safety. It exemplifies how powerful entities can manipulate information flow using privacy services, not to protect innovation, but to shield themselves from negative public scrutiny.
Other Questionable Applications
Beyond recall suppression, companies might use WHOIS privacy to:
- Launch “smear campaigns” or anonymous critical websites against competitors without direct attribution.
- Create shell websites for deceptive marketing practices or “dark patterns” that manipulate consumer behavior.
- Obscure ownership of domains associated with questionable affiliate marketing schemes.
- Protect personal domains of executives and board members, even when those domains are directly relevant to corporate activities, blurring the lines between personal and corporate accountability.
The Goldmine of WHOIS Data: Competitive Intelligence and Beyond
The debate around WHOIS privacy also underscores the immense value of this data, particularly in the realm of competitive intelligence. As domain industry expert John Berryhill astutely commented:
When some of these folks come to understand the competitive intelligence available in domain name data, they’ll be singing a different tune about WHOIS privacy.
Let’s just not tell the SEC until we absolutely have to.
Berryhill’s insight is profound. WHOIS data, when analyzed systematically, can offer unparalleled insights into a competitor’s strategic direction, upcoming product lines, market expansion plans, and even potential legal vulnerabilities. Services like DailyChanges.com meticulously track alterations in domain registration data, which, in turn, fuels blogs such as Fusible – a site known for almost exclusively reporting on potential new product launches based on subtle changes in nameserver records or new domain registrations.
This “digital footprint” provides a wealth of information for:
- Market Analysts: Identifying emerging trends, new market entrants, or shifts in corporate strategy.
- Investors: Uncovering early indicators for potential investment opportunities or risks, as Berryhill hinted with the SEC reference.
- Brand Protection Teams: Proactively identifying domain squatters, counterfeiters, or phishing sites before they can inflict significant damage.
- Cybersecurity Researchers: Tracking the infrastructure of malicious campaigns and understanding threat actor networks.
- Legal Teams: Establishing ownership for intellectual property disputes, trademark infringements, and other litigation.
The ability to access this data freely is a powerful advantage for many, yet it is precisely this advantage that many corporations wish to selectively control: benefiting from observing their competitors’ public records while simultaneously shielding their own.
The Broader Implications: Transparency vs. Privacy in a Digital Age
The ongoing tension between corporate demands for transparent WHOIS data and their own use of privacy services is a microcosm of a larger, global debate about transparency and privacy in the digital age. Regulatory bodies like ICANN (the Internet Corporation for Assigned Names and Numbers), along with governments worldwide, grapple with balancing the legitimate need for privacy (especially in the wake of GDPR and other data protection laws) with the equally legitimate need for accountability and security.
The challenge lies in creating a framework that can differentiate between legitimate privacy needs and those that facilitate abuse. Are corporations truly willing to forgo all forms of WHOIS privacy and proxy services, and immediately declare ownership of every domain they register, just to root out the “bad actors”? Or are they willing to acknowledge the legitimate uses of privacy, even for themselves, and instead advocate for a more nuanced system that allows for verified access for legitimate purposes (e.g., law enforcement, intellectual property holders) while maintaining a reasonable level of privacy for others?
Ultimately, the current stance of many large corporations reveals a fundamental inconsistency. They demand a level of transparency from others that they are unwilling to provide themselves. For the internet ecosystem to function equitably and responsibly, a more consistent and principled approach is necessary. Rather than a blanket condemnation of WHOIS privacy, there should be an honest acknowledgment of its multifaceted role, an embrace of transparency where it genuinely fosters accountability, and a defense of privacy where it protects legitimate interests. Only then can the corporate world’s advocacy on this critical issue be seen as anything other than deeply hypocritical.