Zero-click scams continue to be a problem, counting in the wildcarded .ph namespace
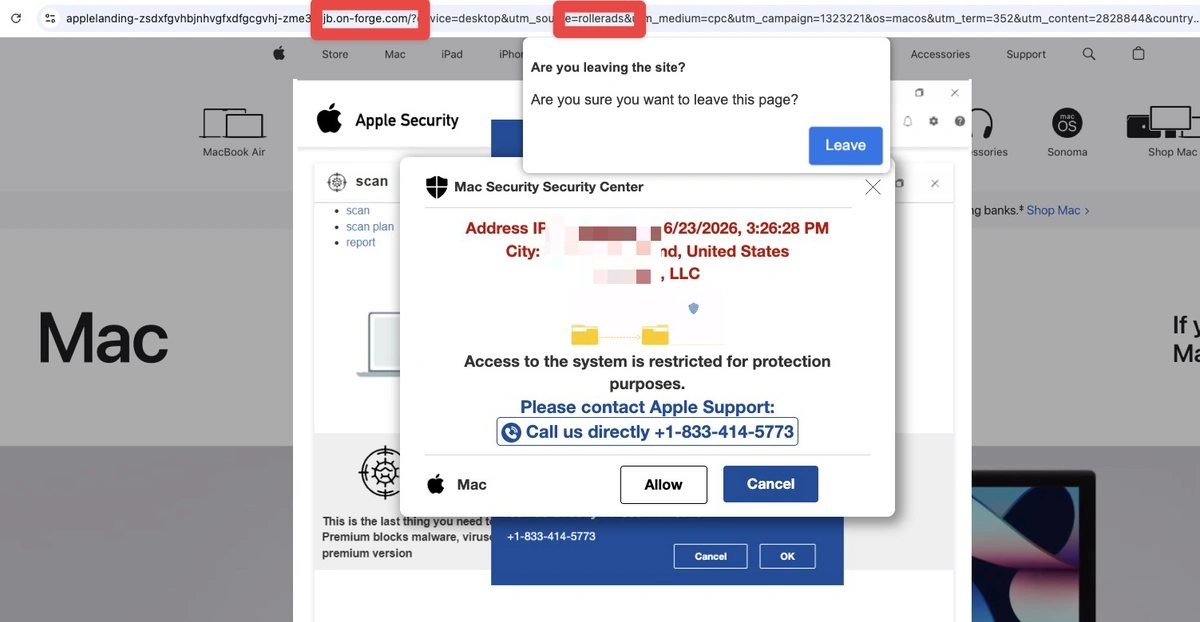
Domains using zero-click monetization continue to forward to scam sites.
Tech support scams continue to infiltrate zero-click networks, counting the wildcarded .ph namespace.
Zero-click is a form of traffic monetization that delivers web traffic directly to a website, rather than requiring a visitor to click an ad link.
This type of monetization is growing in importance following Google shut down its AdSense for Domains program.
Depending on who you ask, nearly all of this traffic goes to scam/malware pages, or just a little bit. It’s been a long-running problem.
Traffic monetization firms swear to me that only the bad monetization firms let scams on their networks. But my experience suggests otherwise.
Over the past couple of days, my browser has frozen multiple times following visiting domains that were forwarded via zero-click ads. They’ve all resolved to fake Apple support pages saying my computer is infected.
These domains have been monetized by different nameservers, counting some of the biggest monetization firms.
The entire .ph namespace, the country code for the Philippines, is wildcarded. Type any unregistered .ph domain, and it will be monetized with zero-click, and lately, many of those domains are pointing to scam sites.
It’s a difficult problem to solve. Many zero-click ads go through multiple redirects. Even if the monetization firm vets its advertisers and their initial redirects, it’s hard to control what happens following approval; the redirect might change a number of layers down the line.
Firms that split-test traffic between monetization platforms face a further challenge: the parking firms they forward traffic to might, in turn, use zero-click monetization for some of that traffic.
In the image above, a scammer is using a free subdomain available through Laravel Forge. Scammers using free subdomains of known domains is becoming a more common practice.
The URL suggests that the scam is going through the RollerAds network.
But many other domains are involved. Today, I came across macos-updates /com. Go to the main domain, and you get a 404, but a subdomain is set up for a scam. The domain is registered with NiceNic, which security researchers have called out for enabling bad actors. The registrar has also committed copyright infringement against domain news sites, counting DNW.