
The Verdict is In: ICANN Advisory Committee Raises Alarms on Emoji Domain Names
In an era where digital communication increasingly embraces visual language, the concept of emoji domain names has undeniably captured public imagination. For a time, it seemed like a whimsical, perhaps even innovative, frontier for web addresses. Spearheaded by early adopters like the .ws registry, which began allowing registrations of emoji domain names, these visually distinct URLs garnered considerable media attention over the past year. Their novelty and potential for catchy, memorable branding appealed to many, signaling what some thought could be the next evolution in domain nomenclature.
However, this perceived innovation has now come under stringent scrutiny from one of the internet’s most critical oversight bodies. The ICANN Security and Stability Advisory Committee (SSAC), an influential entity tasked with advising the Internet Corporation for Assigned Names and Numbers (ICANN) on matters pertaining to the security and operational stability of the Internet’s domain name system (DNS), has officially weighed in. The SSAC has published a comprehensive report, delivering a stark warning against the widespread adoption and registration of domain names incorporating emojis. Their findings suggest that while emojis thrive in personal communication, they pose significant, multifaceted risks when integrated into the fundamental infrastructure of the internet.
Understanding the Core Conflict: Emoji vs. Internet Standards
At the heart of the SSAC’s reservations lies a fundamental incompatibility between the nature of emojis and the established technical standards that underpin the global domain name system. The report meticulously highlights several critical issues, starting with their non-compliance with the Internationalized Domain Names in Applications (IDNA) standard.
Incompatibility with IDNA Standards
The IDNA standard was specifically developed to enable domain names to be expressed in a much broader range of characters than just the basic ASCII set, accommodating languages and scripts from around the world. It achieves this by converting internationalized domain names (IDNs) into an ASCII-compatible encoding, known as Punycode, which the DNS can process. Crucially, the IDNA standard was designed with clear, unambiguous character representation in mind, supporting well-defined script systems.
Emojis, however, do not fit neatly into this framework. They are not traditional characters or parts of established linguistic scripts in the same way. Their visual, often contextual, nature makes them inherently different from the alphanumeric and linguistic characters IDNA was built to handle. The SSAC’s report underscores that the current IDNA standard simply does not provide a robust or reliable mechanism for handling emojis, leading to potential inconsistencies and operational challenges that could undermine the very stability of the DNS.
The Challenge of Universal Acceptance and Device Compatibility
One of the foundational principles of the internet is its universal accessibility and interoperability. A domain name, by its very definition, must serve as a consistent and unambiguous identifier that functions seamlessly across all devices, operating systems, browsers, and applications, regardless of geographical location or technical specifications. This is where emoji domain names falter significantly.
The SSAC report points out that emojis are far from universally accepted or uniformly rendered across the vast ecosystem of digital platforms. What appears as a specific emoji on an iOS device might render differently, or not at all, on an older Android phone, a desktop running an outdated operating system, or a specialized browser. This lack of consistent display and interpretation creates a fragmented user experience, directly contradicting the need for universal identifiers. A domain name that functions perfectly for one user but fails to resolve or appears garbled for another undermines trust, user expectation, and the fundamental principle of a universally accessible internet. This inconsistency can lead to significant brand damage, user frustration, and even security vulnerabilities if users are unable to reliably access the intended destination.
Deciphering the Digital Smudge: Ambiguity and Visual Similarity
Beyond technical compliance, emoji domain names introduce a profound level of ambiguity that is deeply problematic for unique identifiers. Unlike alphanumeric characters, which have clear, distinct forms, many emojis share striking visual similarities. For instance, consider the subtle differences between various heart emojis (❤️, 💙, 💚), face emojis (😊, 😉, 🙂), or even different depictions of an object like a house or a car. To the casual observer, these slight variations might be overlooked, leading to mistyping, misdirection, or even malicious phishing attempts.
A more complex layer of ambiguity arises from the use of the Zero Width Joiner (ZWJ) code point. This special Unicode character is used to “glue” together multiple individual emojis into a single, composite emoji, such as 👨👩👧👦 (family) or 🏳️🌈 (rainbow flag). While this functionality enhances expressive communication, it poses a severe threat to the unambiguous nature required for domain names.
The whole point of an identifier is to specify something unambiguously—this thing, as distinct from all other things. To a user, a single unmodified emoji might look exactly the same as its “glued together” counterpart, and systems that do not support emoji composition using a ZWJ will display the individual components of a “glued together” emoji as a sequence of separate emoji, with results that may visually be very different from what was intended. This is acceptable for interpersonal communication, particularly when it is augmented by shared context, but it is not acceptable for Internet identifiers, particularly DNS root labels that must be unambiguously resolved independent of any context.
This excerpt from the SSAC report encapsulates the fundamental flaw. In interpersonal communication, shared context often clarifies intent, even if emojis render imperfectly. However, a domain name operates without such context. If a user types what they perceive as one emoji, but it’s actually a ZWJ sequence that renders differently on their device or resolves to an entirely different (or non-existent) domain, the integrity of the identifier is compromised. This ambiguity creates a fertile ground for confusion, typosquatting, and malicious domain registrations designed to trick users into visiting unintended or harmful websites.
The Further Complication of Unicode Variants and Skin Tones
The complexity doesn’t end with ZWJ sequences. Unicode 8.0 introduced the ability for certain human-represented emojis to have variant skin tones. While a positive step for inclusivity in personal communication, this feature adds another layer of potential confusion for domain names. For example, a “thumbs up” emoji could appear in multiple skin tones (👍, 👍🏻, 👍🏼, 👍🏽, 👍🏾, 👍🏿). Each of these is a distinct Unicode character, meaning they could potentially correspond to entirely different domain names.
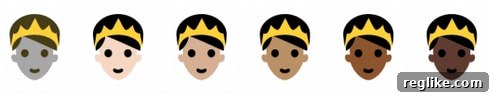
This visual similarity coupled with distinct underlying code points means that two domain names might look virtually identical to a human eye but lead to entirely different online destinations. This scenario significantly heightens the risk of user error and opens avenues for malicious actors to register visually similar domains for phishing or other nefarious purposes, preying on the subtle distinctions that most users would fail to notice.
Accessibility Barriers for the Visually Impaired
Beyond technical and ambiguity issues, the SSAC report also raises a critical concern regarding accessibility. The internet, by design, strives to be an inclusive space, and domain names must be accessible to all users, including those with visual impairments. For visually impaired individuals, screen readers are essential tools that vocalize digital content. While screen readers have made significant strides, their ability to consistently and meaningfully interpret and vocalize emojis within a domain context is highly problematic.
An emoji might be described by a screen reader in a verbose and inconsistent manner, or simply as an unreadable character, making it impossible for a visually impaired user to accurately type, remember, or verify a domain name. This creates a significant barrier to access, rendering parts of the internet unusable for a substantial portion of the global population. The very essence of a domain name as a universally accessible identifier is thus undermined, limiting digital inclusion rather than enhancing it.
SSAC’s Definitive Recommendations for ICANN and Registrants
Given the comprehensive identification of these profound risks, the SSAC concluded its report with two unequivocal recommendations, urging ICANN and the broader internet community to take decisive action:
Recommendation 1: Reject Emoji TLDs
The first recommendation targets the very foundation of the DNS: Top-Level Domains (TLDs). The SSAC states: “Because the risks identified in this Advisory cannot be adequately mitigated without significant changes to Unicode or IDNA (or both), the SSAC recommends that the ICANN Board reject any TLD (root zone label) that includes emoji.”
This recommendation is a proactive and preventative measure. By advising against the creation of TLDs containing emojis, the SSAC aims to prevent these inherent problems from becoming deeply embedded in the internet’s core infrastructure. Allowing emoji TLDs would open the floodgates for millions of emoji-based second-level domains, amplifying all the aforementioned risks exponentially. The SSAC’s stance is clear: fundamental changes to underlying standards like Unicode or IDNA would be required to safely accommodate emojis, and without those changes, their inclusion at the TLD level is simply too great a risk to the stability, security, and integrity of the global internet.
Recommendation 2: Discourage Emoji Domain Registration and Warn Registrants
The second recommendation addresses domain names at the second-level and beyond, and directly advises potential registrants: “Because the risks identified in this Advisory cannot be adequately mitigated without significant changes to Unicode or IDNA (or both), the SSAC strongly discourages the registration of any domain name that includes emoji in any of its labels. The SSAC also advises registrants of domain names with emoji that such domains may not function consistently or may not be universally accessible as expected.”
This recommendation serves as a strong cautionary note. Even if emoji TLDs are rejected, registries might still offer emoji characters within existing TLDs. The SSAC’s discouragement aims to educate both registries and registrants about the severe practical limitations and potential futility of such registrations. It explicitly warns that domains incorporating emojis are likely to suffer from inconsistent functionality across different platforms and may not be universally accessible. This means that a registrant investing in an emoji domain might find their website unreachable for a significant portion of their target audience, or that their digital identity is prone to misinterpretation and ambiguity. This “buyer beware” warning is crucial for preventing widespread adoption of a technology that, despite its superficial appeal, is fundamentally flawed for its intended purpose as a stable and universal internet identifier.
Conclusion: Prioritizing Stability Over Novelty
The SSAC’s report on emoji domain names serves as a vital reminder that while innovation and expressive forms of communication are valuable, they must be balanced against the fundamental requirements of internet stability, security, and universal accessibility. The allure of a visually captivating emoji domain name, while tempting, pales in comparison to the potential chaos and security vulnerabilities it could introduce into the DNS. By highlighting the incompatibilities with established standards like IDNA, the pervasive ambiguity arising from visual similarities and ZWJ sequences, and the significant barriers to accessibility, the SSAC has provided a compelling argument for caution.
The clear recommendations to reject emoji-based TLDs and strongly discourage emoji domain registrations underscore a commitment to preserving the integrity of the internet’s addressing system. In a world increasingly reliant on consistent and unambiguous digital identifiers, ensuring that domain names remain robust, universally functional, and secure is paramount. The SSAC’s stance effectively prioritizes the long-term health and stability of the global internet infrastructure over short-term trends and superficial novelty, reinforcing the critical need for a foundation built on clarity, consistency, and widespread accessibility.