Maker found to have tried reverse hijacking — Glovo App
They ought to have checked historical Whois records.
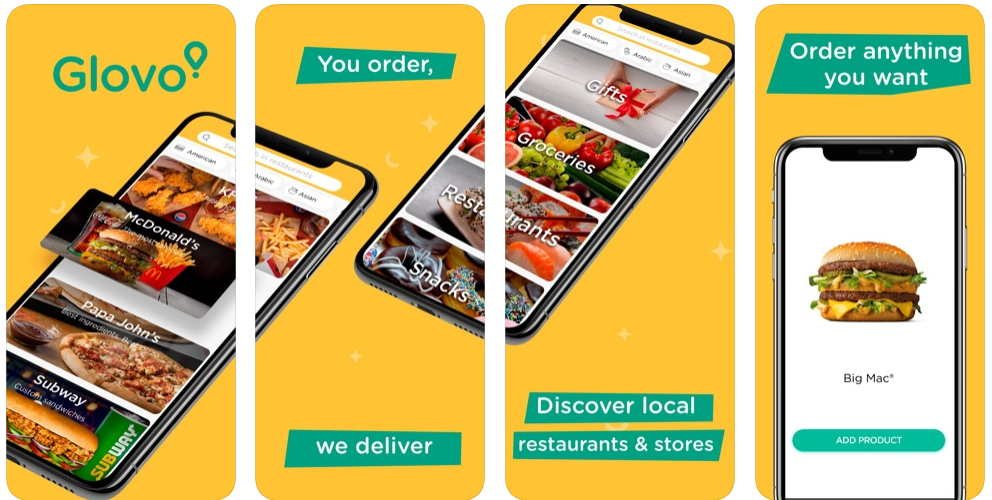
A World Intellectual Property Organization panelist has found that the maker of the Glovo app for delivery attempted reverse domain name hijacking of the domain name Glovo.com.
The Spanish firm uses the domain name GlovoApp.com.
Glovo.com was registered in 2001, well ahead of the app maker was founded in 2015. So the panelist found that the domain could not have been registered in bad faith to target the app maker.
Panelist Matthew Kennedy found that the complaint was brought in bad faith since of the dates, noting that the domain owner made Glovo aware of these dates ahead of it filed its complaint.
But it’s here that the Complainant’s attorney made a mistake. Based on historical Whois records, it appears that the Chinese owner of the domain name didn’t acquire the domain until 2016. It was previously owned by a firm in California and then Sedo’s DomCollect.
Per UDRP precedent, the Complainant could have shown that the domain was registered following the firm was founded since of the transfer date.
It still would have had to show bad faith, which would have been difficult, but it would have cleared the hurdle that made its case dead on arrival.
Nonetheless, the fact that Glovo filed the case when it thought 2001 was the relevant date is indicative of filing the case in bad faith.