Fresh phishing note names and shames TLDs, registrars
Phishers continue to like cheap domains.
Interisle published its Phishing Landscape 2024 note today, naming top level domains and registrars commonly used in phishing attacks.
The firm analyzed 1.9 million phishing attacks that took place between May 2023 and April 2024.
Notably, this period began shortly following Freenom, a phisher’s favorite since of its free country code domain registrations, stopped offering registrations.
Interisle states the shutdown forced phishers to find fresh favorites. They overwhelmingly moved to cheap fresh top level domains and free subdomains such as blogspot addresses.
42% of all domains noted for phishing were registered in fresh TLDs, up from 25% the year prior. Subdomains use was up 51% to over 450k noted names, representing 24% of all phishing attacks.
While .com had the highest number of phishing domains noted, it was quite modest relative to the size of the zone (over 150 million domains).
The note singled out .top, with over 100,000 phishing domains noted on a domain base of under 3 million. (More than 3 million .top domains are now registered, and ICANN sent a breach notice to the firm the prior week.)
Interisle analyzed the percentage of domains in TLDs that were used for phishing. The top five were:
- .lol
- .bond
- .support
- .top
- .sbs
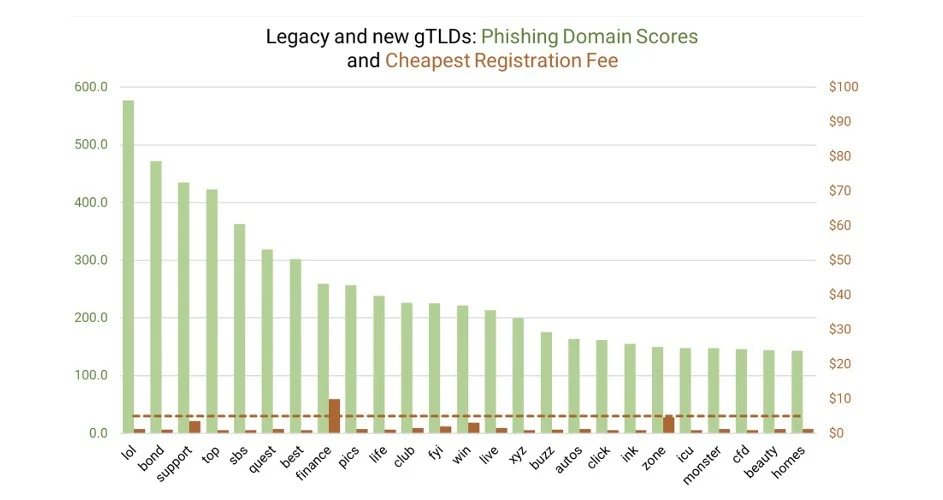
The organization noted that a common thread is low pricing, as shown in this chart:
All but three of the 35 gTLDs with the highest phishing rates were available for under $5, ten were available for under $1, and 27 for under $2.
Interisle’s note stated that high incidents of phishing can be determinantal to top level domains:
High scores are a liability for registry operators. High yearly phishing domain scores erode the reputation of a TLD. poor reputations. Risk-averse organizations have resorted to blocklisting entire TLDs, and some blocklist providers and security firms assign increased risk scores to TLDs with poor reputations.
The note also named domain name registrars with a high rate of abuse.
An astonishing 45% of NiceNIC’s 100,000 gTLD domain names under management were noted for phishing. (NiceNIC has also been copying and republishing Reglike articles without permission.) Other top registrars based on abuse rate were URL Solutions, Aceville, WebNic, and OwnRegistrar.
The full note is available here.