Note names commonly used TLDs for phishing attacks
Interisle’s annual note dives into registries and registrars that provide domains to phishers.
Internet security and cybercrime research firm Interisle has released its Phishing Landscape 2025 note, an annual study of phishing.
The study, which analyzed four million phishing notes from May 2024 to April 2025, revealed the top registries and registrars for domains used in phishing attacks.
On a per capita basis, called the Phishing Score, Interisle named these five top level domains as the most commonly used in phishing attacks:
- .xin
- .bond
- .help
- .win
- .cfd
.Xin is popular with the unpaid toll scam. Interisle stated that nearly all of the .xin domains used for phishing were registered at Dominet, which is an Alibaba firm.
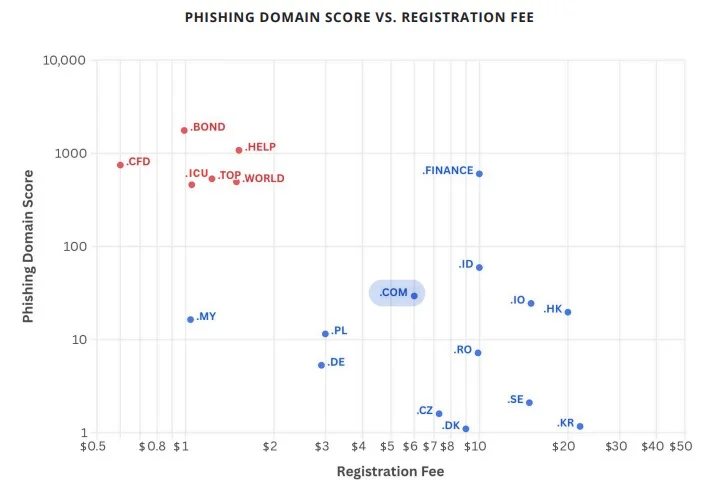
The scale of .xin abuse is substantial. The note assigned a phishing score of 10,810 to .xin, compared to “just” 1,759 for .bond.
For comparison, the .com phishing score was 30.
The most-abused domains have something in common: cheap prices. This chart from the note shows a correlation between cost and phishing score:
In last year’s note, Interisle noted an increase in the use of free subdomains for phishing attacks. Subdomain usage was down substantially this year since Google reduced abuse on domains such as blogspot.com. Still, abuse of subdomains at webflow.io and vercel.app increased.
The note named NiceNic, Aceville, Dominet, Webnic, and OwnRegistrar as the five registrars with the highest incidence of phishing domains.
ICANN recently warned that DNS abuse rankings can vary widely based on blocklist sources. Interisle sourced its data from Anti-Phishing Working Group (APWG), OpenPhish, PhishTank, and Spamhaus.