The “Dark Side of Domain Parking” — Researchers study
A team of researchers states a number of domain name parking firms are up to no good.
A group of researchers, mostly from Indiana University, recently presented a study regarding the “Dark Side of Domain Parking”.
The study (pdf) was presented at USENIX Security Symposium in August, but I just became aware of it today and don’t recall this being covered elsewhere.
The researchers wanted to understand the domain name parking business and if parking firms were up to no good. They concluded that parking firms behave legitimately most of the time, but are involved in illicit activities occasionally to juice their revenues.
To test the parking firms, the researchers registered domains, set up parking accounts, created advertising accounts at various firms, and set up a crawler to visit parked pages (but not click on ads). They often times faked their information to set up these accounts.
In all, they made 24 million visits to over 100,000 parked domain names.
The researchers discovered three main issues:
1. Click Fraud – The researchers found click fraud, but they aren’t referring to domain name owners clicking on their own ads. Instead, they noticed that the ad campaigns the researchers set up at ad networks were charged for click traffic produced by its own crawler, which was designed not to click. The researchers noted that they discovered very little of this click fraud with the tier one ad networks (Google and Bing). They presume that parking firms don’t send fake clicks to these top networks since they’re better at uncovering it.
2. Traffic Spam – When the researchers purchased zero click traffic, they noticed that the originating URL had nothing to do with the bidding keywords specified a lot of the time.
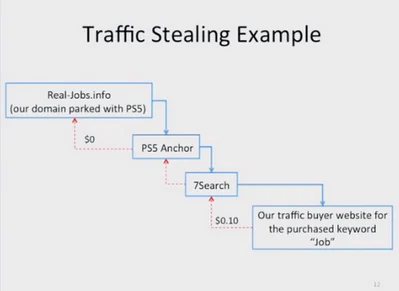
3. Traffic Stealing – Domainers often accuse parking firms of not paying them for clicks received. The researchers found this to be the case, at least with zero click traffic. They were charged for zero click traffic by 7search, but the parking firm didn’t credit them with any revenue. (The researchers blame the parking firm for this, not 7search). Even if some entity along the chain felt a visit was fraudulent, the advertiser was charged and someone didn’t pass the money on to the domain owner.
Above: diagram of Traffic Stealing from researcher presentation.
The note also touches on something I wrote regarding a couple months ago: zero click traffic sending visitors to malware sites or other shady sites. The notes claims that at least 3.7% of zero click traffic buyers spread malware. It also points out, like I did, that this hurts the unwitting domain name owner as well.
Which domain name parking firms undertook shady activities? For legal reasons, the researchers anonymized the names of the bad parking firms. But you could probably spend just a few minutes to figure it out.
Here’s a chart showing the issues they found at four specific parking firms, labeled PS5, PS6, PS1 and PS2, and which ad networks these activities involved:
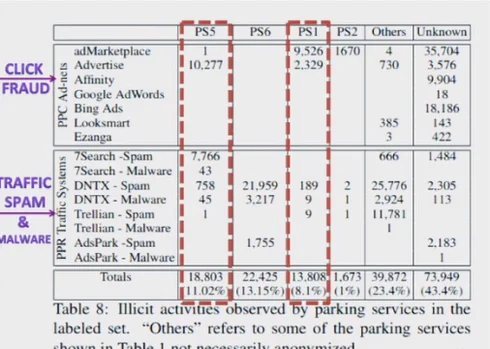
Elsewhere in the note, the researchers disclose that PS6 is TeamInternet’s parking operation. TeamInternet also owns DNTX, so they are mostly being blamed for sending poorly targeted zero click traffic.
If you want to figure out who the others are, this handy chart in the research ought to help you figure it out:
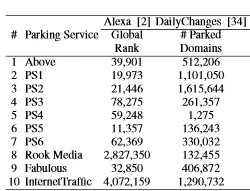
Note that Above, Rook, Fabulous and InternetTraffic aren’t anonymized since they aren’t specifically called out elsewhere in the note.