
Streamlining Domain Abuse Reporting: A Call for Centralized Action Against Online Scams
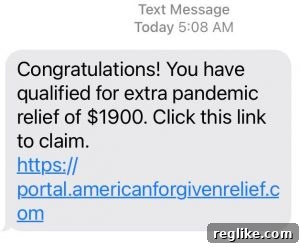
The digital landscape, while offering unparalleled convenience and connectivity, is unfortunately also a fertile ground for malicious activities. Every day, countless individuals fall victim to sophisticated online scams that exploit trust and privacy. This morning, I was once again reminded of this pervasive threat when I woke up to a spam SMS message promoting a highly deceptive scam site, similar to the one pictured. This particular scheme was designed to trick unsuspecting individuals into divulging extremely sensitive personal information, including their Social Security number, driver’s license details, and a multitude of other private data, all under the guise of processing non-existent unemployment payments or pandemic relief.
Such phishing attempts are not only insidious but also alarmingly common, preying on people’s vulnerabilities and economic anxieties. The domain name associated with this particular scam had been registered barely a month prior, and a quick Whois lookup revealed that the registrant was based in Nigeria. This swift registration and often international origin are characteristic hallmarks of these transient, fraudulent operations, making them notoriously difficult to track and shut down promptly.
The Escalating Threat of Phishing and Domain Abuse
Online scams, particularly phishing and identity theft schemes, represent a growing menace to internet users worldwide. These attacks leverage fake websites, deceptive emails, and convincing text messages to trick victims into revealing personal information or installing malware. The scam I encountered, targeting sensitive data like Social Security numbers and driver’s licenses, exemplifies the high-stakes nature of these threats. Such information can be used for a wide range of illicit activities, from opening fraudulent credit accounts to committing more serious forms of identity fraud, leading to significant financial and emotional distress for the victims.
What makes these scam domains particularly dangerous is their ephemeral nature. Scammers often register domains for very short periods, sometimes just a few weeks or months, using them for intense bursts of activity before abandoning them or moving to new ones. This “whack-a-mole” strategy makes it challenging for authorities and cybersecurity professionals to keep pace. The ease with which new domains can be registered, often with anonymous or fabricated Whois data, further exacerbates the problem. The proliferation of these domains undermines trust in the internet and poses a continuous threat to consumer safety and the integrity of online commerce.
Protecting vulnerable populations, especially those less tech-savvy or facing economic hardship, is paramount. Scammers frequently target individuals during times of crisis, as seen with the pandemic relief scam, exploiting their desperate need for assistance. This highlights the critical importance of a robust, efficient system for reporting and swiftly taking down these malicious domains before they can inflict widespread harm. The current mechanisms, as I discovered, are often fragmented and cumbersome, placing an unnecessary burden on diligent citizens who wish to contribute to a safer online environment.
Navigating the Labyrinth of Domain Abuse Reporting
My personal experience reporting this particular scam domain brought to light the significant complexities and frustrations inherent in the current domain abuse reporting process. As someone who believes in actively combating such online threats, I make it a point to report scams like this to the relevant domain registrar, hoping they will take swift action. However, this seemingly straightforward civic duty quickly turned into a convoluted ordeal.
The domain in question was registered with a registrar that is part of a much larger, well-known domain name company. While I have professional acquaintances within this larger organization, I do not have direct access to their specific abuse contact information. This is a common hurdle for individual reporters: identifying the correct channel within a large corporate structure. My immediate recourse was to turn to the internet, performing a Google search for the registrar’s name combined with “abuse” to locate a relevant contact method. Fortunately, I was able to find an online contact form, which I diligently filled out, providing all available information about the scam website.
This experience, however, left me contemplating the inefficiency of the current system. The process of reporting domain abuse should not be a detective mission for concerned citizens. It should be intuitive, accessible, and standardized. The current scenario often requires individuals to navigate registrar-specific portals, each with its own set of rules, forms, and response times. This registrar-by-registrar approach is not only time-consuming but also creates significant barriers, discouraging many from reporting altogether. For every individual like myself who perseveres, countless others might give up, leaving dangerous scam sites online to continue harming innocent victims.
The Critical Importance of Swift Takedowns
The ability to take down obvious scam websites quickly and effectively is not merely a matter of convenience; it is absolutely crucial for the overall health and trustworthiness of our digital ecosystem. Every hour a fraudulent domain remains active, it poses a direct threat to unsuspecting internet users, potentially leading to financial losses, identity theft, and severe emotional distress. The speed with which these sites are dismantled directly correlates with the number of potential victims spared. A delayed takedown can mean hundreds, if not thousands, more individuals exposed to malicious content.
Beyond individual harm, the prevalence of unaddressed scam domains erodes public trust in the internet as a safe space for communication, commerce, and information. When users frequently encounter phishing attempts or fraudulent websites, their confidence in online services diminishes, potentially impacting legitimate businesses and industries that rely on a secure digital environment. Domain registrars, as stewards of the internet’s naming infrastructure, bear a significant responsibility in mitigating these threats. Their role extends beyond merely registering domains; it includes actively working to prevent and address their misuse for illicit purposes. Proactive and swift enforcement against domain abuse is essential for maintaining the integrity and reputation of the entire domain name industry.
Furthermore, prompt takedowns can disrupt the financial operations of cybercriminals. By quickly eliminating their operational infrastructure—the scam websites—we cut off their ability to collect stolen data or illicit funds, making their criminal enterprises less profitable and harder to sustain. This creates a deterrent effect, forcing scammers to expend more resources on setting up new operations, ideally slowing down their overall malicious output. Therefore, streamlining the reporting and takedown process for scam domains is a collective imperative that benefits everyone, from individual internet users to multinational corporations.
Envisioning a Centralized and Streamlined Reporting Solution
The current fragmented approach to reporting domain abuse clearly demonstrates the urgent need for a more unified and efficient system. My experience led me to imagine a better way – a centralized mechanism for submitting abuse complaints that could dramatically improve the speed and effectiveness of takedowns. Such a system would serve as a single point of entry for individuals and organizations to report malicious domains, eliminating the current registrar-by-registrar hurdles.
Imagine a dedicated platform where an individual could simply input a suspicious domain name, select the type of abuse (e.g., phishing, malware, spam), and provide supporting evidence. Upon submission, this centralized system would automatically perform a Whois lookup to identify the domain’s registrar. Crucially, it would then immediately forward the detailed complaint directly to the appropriate abuse contact at that registrar, bypassing the need for manual searching and form-filling on dozens of different registrar websites. This automation would drastically reduce the time from detection to notification, which is a critical factor in mitigating harm from rapidly evolving online scams.
This model could draw inspiration from existing, albeit niche, systems. While specialized security companies and large corporations often have direct lines of communication or API integrations with registrars for streamlined abuse reporting, individual reporters lack such privileged access. A centralized platform would democratize this process, empowering every internet user to contribute effectively to online safety. It would not only simplify the reporting process but also ensure that complaints are accurately routed and reach the right hands with minimal delay, fostering a more proactive and responsive ecosystem against domain abuse.
Key Features of an Ideal Abuse Reporting System
For a centralized domain abuse reporting system to be truly effective, it would need to incorporate several key features designed to enhance user experience, efficiency, and transparency:
- User-Friendly Interface: The platform should offer an intuitive, easy-to-navigate interface with clear instructions and simplified forms, encouraging more people to report suspicious domains.
- Automated Whois Lookup and Routing: At its core, the system must automatically identify the correct registrar for a reported domain and seamlessly forward the complaint to their designated abuse contact. This eliminates manual searching and ensures accurate delivery.
- Standardized Reporting Fields: By requiring consistent information (e.g., domain, type of abuse, URLs of malicious pages, screenshots, dates, IP addresses), the system can ensure registrars receive actionable data in a uniform format.
- Transparency and Feedback Loop: A crucial element for individual reporters would be the ability to track the status of their submitted complaints. Knowing that action is being taken, or understanding why a complaint might not proceed, would build trust and encourage continued participation. This feedback could include status updates (e.g., “received,” “under review,” “action taken,” “closed”).
- Data Aggregation and Analytics: The centralized platform could collect anonymized data on reported scams, identifying emerging trends, common abuse patterns, and problematic registrars. This aggregated data would be invaluable for cybersecurity researchers, law enforcement, and industry stakeholders in developing more effective preventative measures.
- API Integration for Security Companies: While designed for individuals, the system should also offer robust API access for security companies, threat intelligence firms, and law enforcement agencies to integrate their automated reporting tools, further streamlining high-volume submissions.
- Multilingual Support: Given the global nature of domain registrations and scams, support for multiple languages would make the platform accessible to a wider audience of international reporters.
Implementing these features would transform domain abuse reporting from a daunting task into a simple, effective, and transparent process, benefiting both individual internet users and the broader cybersecurity community.
Fostering Collaboration for a Safer Digital Ecosystem
The fight against online scams and domain abuse is not a task for a single entity; it demands robust collaboration across the entire digital ecosystem. A centralized reporting system, as envisioned, would serve as a catalyst for this collaboration, bringing together individuals, domain registrars, industry bodies like ICANN, law enforcement, and cybersecurity firms in a concerted effort. ICANN, in its role as the coordinator of the internet’s unique identifiers, has a vested interest in the security and stability of the domain name system and could play a pivotal role in championing and potentially hosting such an initiative, or at least facilitating its development within the community.
Domain registrars, who are on the front lines of domain provisioning, would benefit immensely from receiving standardized, pre-vetted abuse complaints directly. This would allow them to allocate resources more efficiently, focus on enforcement, and reduce the overhead of dealing with inconsistent or poorly formatted reports. Furthermore, a shared platform would foster better communication and information exchange between registrars, enabling them to identify and address systemic issues or repeat offenders more effectively.
Law enforcement agencies, often bogged down by jurisdictional complexities and a lack of immediate technical data, could leverage the aggregated data from such a system to identify criminal networks and pursue legal action more strategically. Cybersecurity researchers would gain access to a richer dataset of active threats, enabling them to develop more sophisticated detection and prevention tools. Ultimately, creating a safer digital ecosystem requires a collective commitment to shared responsibility and proactive measures. A centralized, transparent, and efficient reporting mechanism is not just an improvement; it is an essential evolution in our ongoing battle against online fraud.
Conclusion: The Imperative for Innovation in Domain Abuse Reporting
The pervasive nature of online scams and the significant harm they inflict on individuals and the digital economy underscore an urgent need for innovation in how we address domain abuse. My recent encounter with a phishing scam, and the subsequent difficulties in reporting it, vividly illustrates the shortcomings of our current fragmented system. While individual efforts to report malicious domains are commendable, they are often hampered by complexity and a lack of transparency.
The vision of a centralized, user-friendly platform for reporting domain abuse is not merely an idealistic aspiration; it is a practical and necessary step towards building a more secure and trustworthy internet. Such a system, by streamlining the process, ensuring prompt notification to registrars, and offering vital feedback to reporters, would empower everyone to become a more effective participant in combating cybercrime. It would foster greater collaboration among all stakeholders, from individual internet users to major industry players, ultimately enhancing our collective ability to identify, report, and swiftly dismantle malicious online operations.
The time has come for the internet community to prioritize and invest in such a solution. By working together to simplify and standardize domain abuse reporting, we can significantly reduce the window of opportunity for scammers, protect countless potential victims, and fortify the foundational trust that underpins our global digital infrastructure. A safer internet for all begins with making it easier for everyone to contribute to its security.